Where data lives, who sees it, who consented:
all under your control.
In Prozence, employee and customer data lives where the company chooses, and who sees what is set module by module. The records privacy law requires are kept inside the product.
You choose
where your data lives.
One product, two ways to run it. You can move from one to the other later.
On your own server
Prozence installs on your company's WordPress site as a plugin. The data stays in your own database; backups and access follow your policies.
- WordPress 6.4+ and PHP 8.1+
- Outside services are used only when you connect them
- Business cards keep working if the licence ends
In the Prozence cloud
Your company gets its own space. We manage updates, backups and server security.
- A separate space and database tables for each company
- Daily backups and updates
- A dedicated server on Enterprise
From notice to deletion,
the record is in the product.
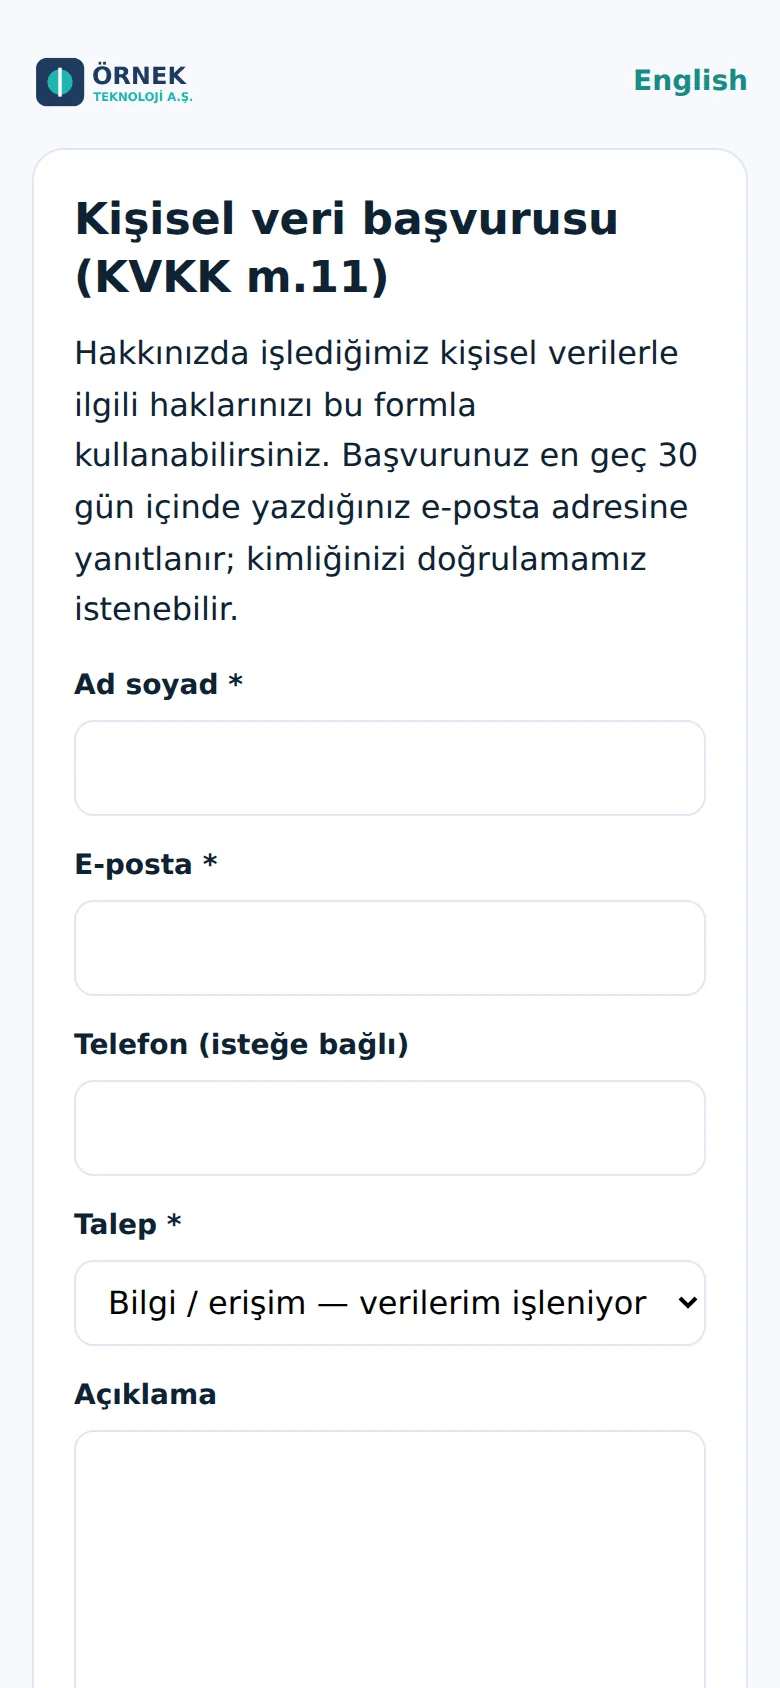
Every flow that processes personal data is tied to a versioned privacy notice and a recorded consent. Data subject requests are tracked against a 30-day deadline.
Versioned texts
Privacy and marketing consent texts; every change becomes a new version and old versions stay readable.
Proof of consent
Which channel, which text version, when, and who recorded it. IP addresses and browser data are not kept.
Request form
Access, correction, deletion, objection and consent withdrawal, with a reference number and 30-day tracking.
Retention and anonymisation
Expired records are listed and anonymised in bulk or automatically every day.
Record of processing
A draft with recipients and international transfers based on the integrations you connect.
Audit log
Text changes, exports, anonymisation and deletions are logged.
Everyone sees only
what their job needs.
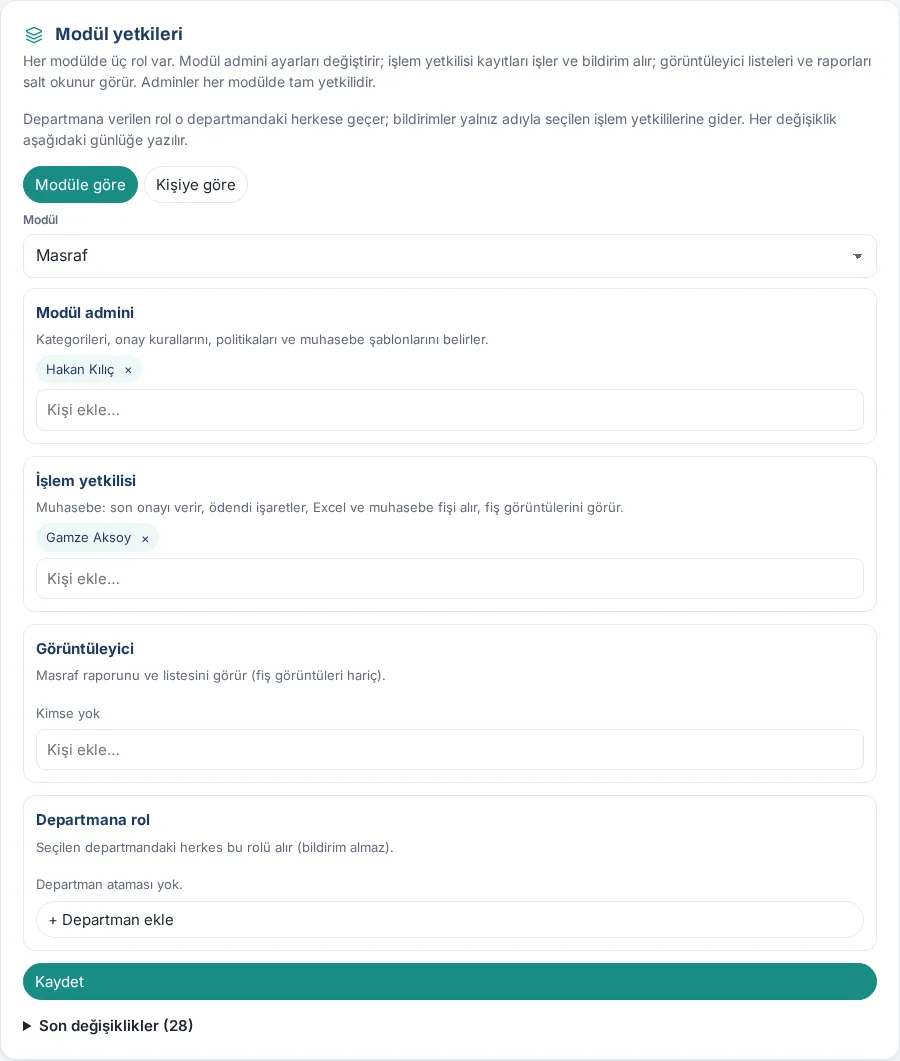
Permissions are granted module by module. A customer record is visible only to the person who added it until it is explicitly shared.
Single sign-on
Google, Microsoft Entra ID and SAML 2.0. Identity tokens are checked for signature, tenant and expiry.
Sign-in by code
A 6-digit code valid for 10 minutes sent to the work email, with attempt limits and protection against account discovery.
Separation of duties
Nobody can approve their own leave request, banner or signature change.
Ownership isolation
Someone else's customer record cannot be claimed or read just by knowing an email or phone number.
Change logs
Permission, signature and settings changes are kept with who made them and when.
Secret keys
API keys and certificates are never returned to the browser; only the last four characters are shown.
Protection against attacks,
layer by layer.
Every public endpoint is limited against abuse. Files and links have unguessable names and are served only to authorised people.
Rate limits
Honeypot fields, timing and per-IP limits on public forms; per-user limits on REST endpoints.
File safety
Uploaded file types are checked from their bytes; images are processed within size limits.
Security headers
nosniff, a strict Referrer-Policy, framing protection and a restricted permissions policy.
Internal network blocking
Webhooks and notifications cannot send requests to internal network addresses.
Signed webhooks
Events sent to outside systems are signed with HMAC-SHA256.
No traces on devices
Personal pages are not cached; app traces on the device are cleared on sign-out.
AI works only
when you switch it on.
Card reading, summaries and enrichment use an AI service (Anthropic Claude). The service is enabled by a company setting, and employees see a note about international data transfer.
Suggestions, not automatic changes
Job change and enrichment suggestions apply only once you approve them.
Labelled content
Everything AI generates carries a note saying so.
No sensitive data
Information about people comes only from public professional sources; private life and sensitive categories are never searched.
Not stored
The card photo a visitor takes when leaving their details and the audio of voice notes are not stored.
Processed in the browser
The background of corporate profile photos is removed entirely in the browser; no face recognition is used.
Daily limits
A daily usage limit and cap are set at company level.
Made to help employees,
not to watch them.
Sensitive features such as attendance and location are enabled by a company setting and are off by default. Anonymous tools really are anonymous.
Location only with consent
Field location tracking needs explicit consent and works only during working hours.
Off by default
Location, Wi-Fi and photo checks for attendance are not used unless the company turns them on.
Real anonymity
In anonymous suggestions, complaints and pulse surveys the sender is never stored; small groups are merged.
Minimal data
Leave requests don't record the reason; "I'm safe" data is deleted when the check-in ends.
Encrypted doctor messages
Messages with the workplace doctor are end-to-end encrypted.
See your own data
Employees can see their own permissions and who can see which of their details in the app.
Your workplace's
new common ground.
Bring your people, your brand and your daily work together. Free for 14 days, no credit card.